
Code signing
Explore all articles and insights related to Code signing.
Category Posts
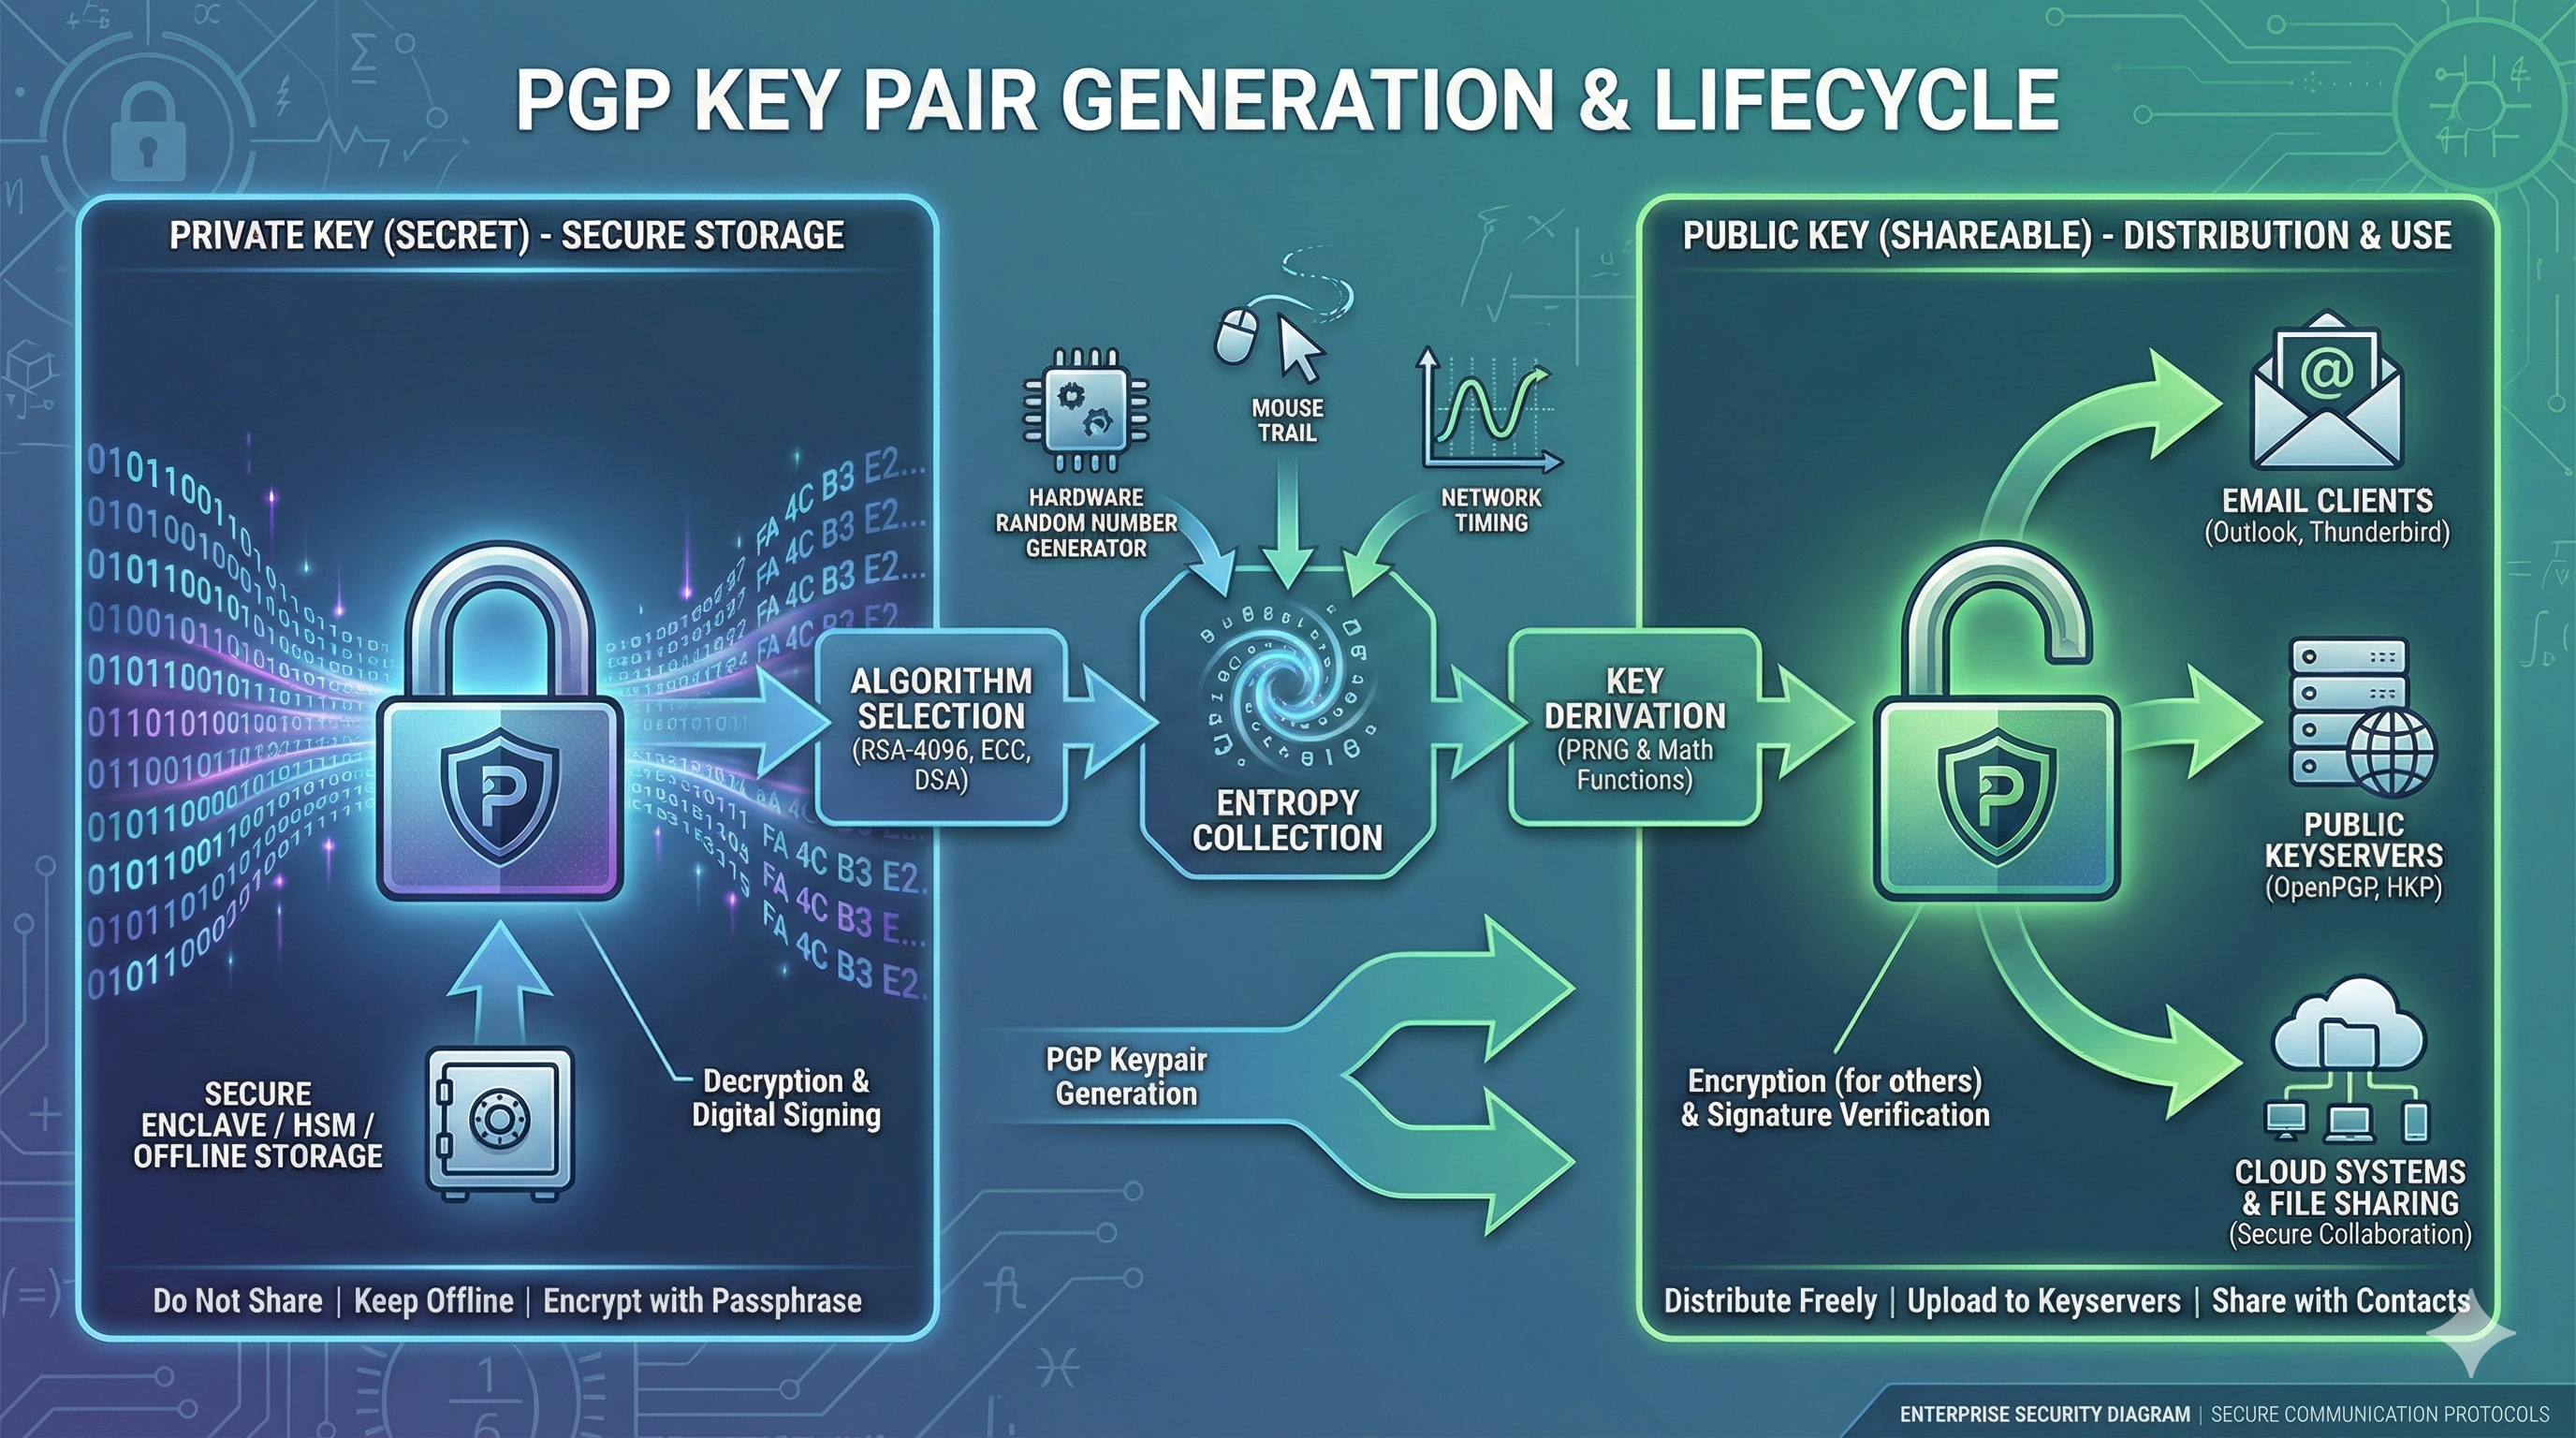
How To Generate PGP Key Pair (2025 Complete Guide)
Generate secure PGP key pairs with GPG, Kleopatra, and CLI tools. Best practices for Windows, Linux, macOS, and enterprise key management.
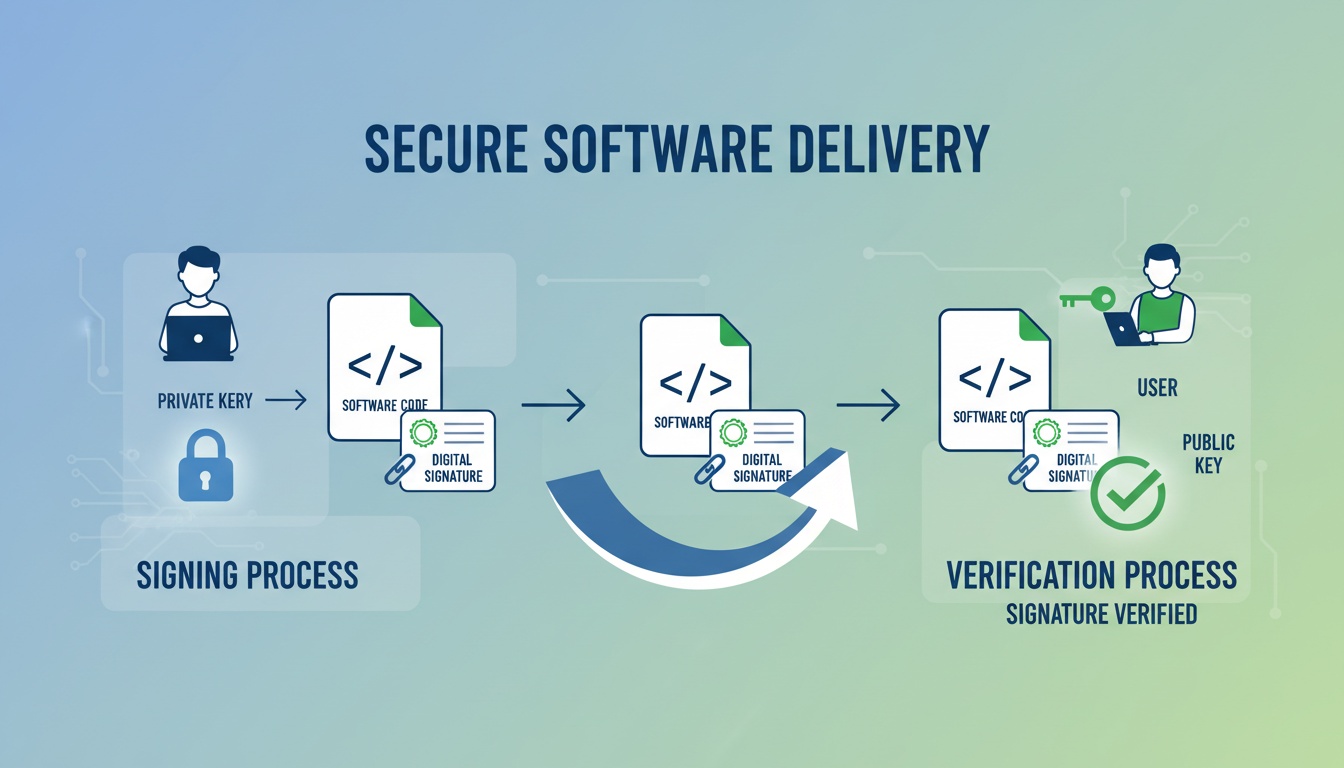
What Is Code Signing? The Enterprise Guide to Supply Chain Trust
Learn what code signing is, how it works, and why enterprises rely on it to secure software, CI/CD pipelines, and trust.
Code Signing and Software Supply Chain Security: A Complete Guide
Code signing proves software authenticity and integrity. Here's how to implement it across CI/CD pipelines, protect signing keys, and defend against supply chain attacks like SolarWinds and xz-utils.
Best Code Signing Platforms 2026: Enterprise Comparison
Compare the best code signing platforms for enterprise — DigiCert, Sectigo, Keyfactor SignServer, Sigstore/Cosign, QCecuring, and Azure SignTool. Covers HSM-backed signing, CI/CD integration, EV certificates, and keyless signing.
Code Signing in Linux: Complete Guide to Signing Packages, Binaries, and Containers
Learn how to sign Linux artifacts including RPM/DEB packages, kernel modules, container images, Git commits, and AppImages. Covers GPG, cosign, Sigstore, and CI/CD integration.
QCecuring vs DigiCert Software Trust Manager: Code Signing Compared (2026)
Compare QCecuring Code Signing vs DigiCert Software Trust Manager for enterprise code signing. Covers DigiCert's deprecation timeline, KeyLocker cloud HSM, CI/CD integration, pricing, and QCecuring's CA-agnostic policy-driven approach.
QCecuring vs Keyfactor SignServer: Enterprise Code Signing Compared (2026)
Compare QCecuring Code Signing vs Keyfactor SignServer for enterprise code signing. Covers SignServer's open-source model, Java-based architecture, on-premises deployment, PQ HSM support, and QCecuring's managed platform with policy engine and CLM integration.
Sigstore Cosign Keyless Signing with GitHub Actions OIDC: Complete Guide
Implement keyless container image signing with Sigstore Cosign and GitHub Actions OIDC. Covers setup, verification, policy enforcement, SLSA provenance, and production deployment patterns.
Post-Quantum Code Signing: Why Firmware and Software Signatures Migrate First
Code signing is the most urgent post-quantum migration almost nobody is planning. A signature made today must stay valid for the decade-plus lifetime of the firmware it protects. Here is why, and how to prepare.
When a Code Signing Key Is Compromised: The Response Playbook
A leaked code signing key is worse than a leaked TLS key because the signatures persist. Here is the containment, revocation reality, re-signing, and forensic playbook.
Code Signing in CI/CD with Ephemeral Keys (Keyless Signing Done Right)
Long-lived signing keys in CI are a liability. Keyless signing swaps them for OIDC identity, short-lived certs, and a transparency log, keeping secrets out of the pipeline.
Ready to Secure Your Enterprise?
Experience how our cryptographic solutions simplify, centralize, and automate identity management for your entire organization.